Brief
Project overview
Company knowledge usually lives with the people who built it, or scattered across file shares, emails, and wikis nobody outside the department can find. This project turns that into a single curated map any employee can read, without exposing the systems behind it.
The design is governance-first. The technical wiki stays private. A page reaches the map only when its frontmatter carries an explicit public visibility tag. Everything untagged is confidential by default, and anything genuinely sensitive is simply never tagged, so the safe state is the default state rather than an exception someone has to remember to apply.
Publishing runs as a reviewed pipeline, not a direct publish:
- Tagged wiki pages are drafted into plain-language sister pages on an hourly schedule by a low-cost LLM, using structured output and no IT detail
- Drafts land in a pull request review queue; nothing appears on the map until a person merges it
- Removing the tag in the wiki removes the page on the next run
- Hand-edited pages can be locked, so automated runs report the change instead of overwriting it
A safety scan runs at every step. Any page containing an internal hostname, IP address, credential, MAC address, share path, or email address is refused outright regardless of its tag. The map itself is read-only and sits behind company single sign-on.
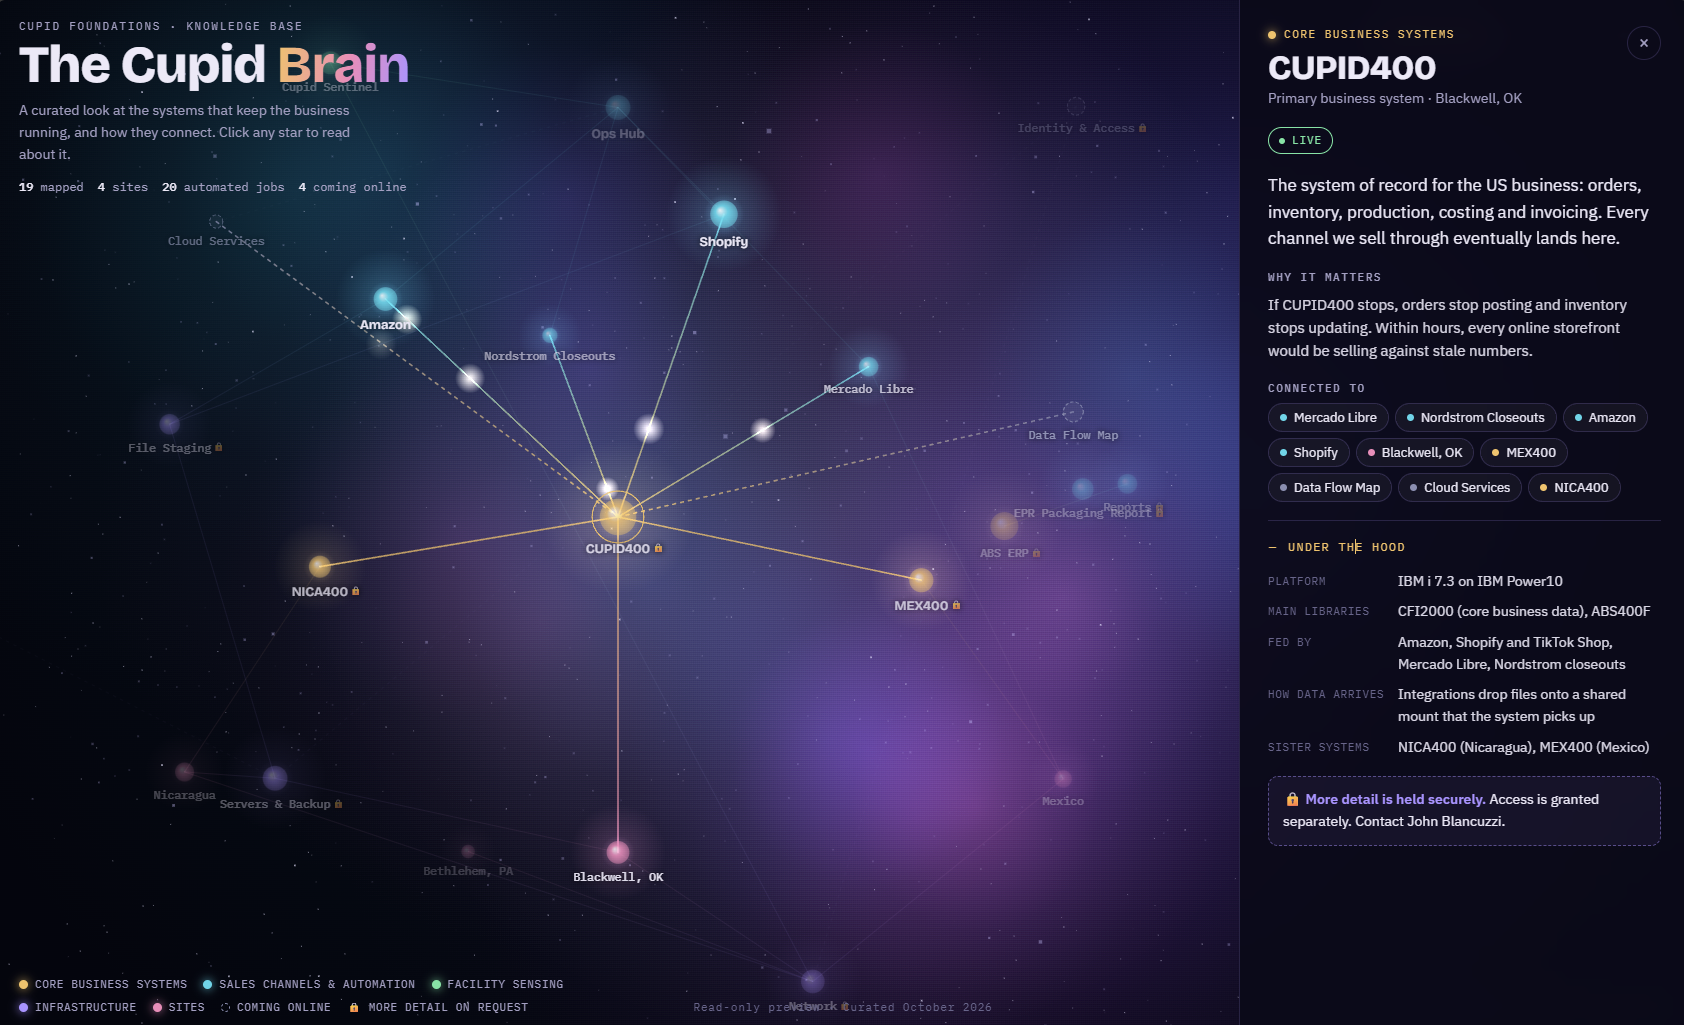
Four visibility levels let one pipeline serve different audiences: information any employee can see, information available to staff on request, information limited to IT and the data team, and information whose existence is never hinted at outside security. Topics with more detail behind them show a lock instead of a dead end.
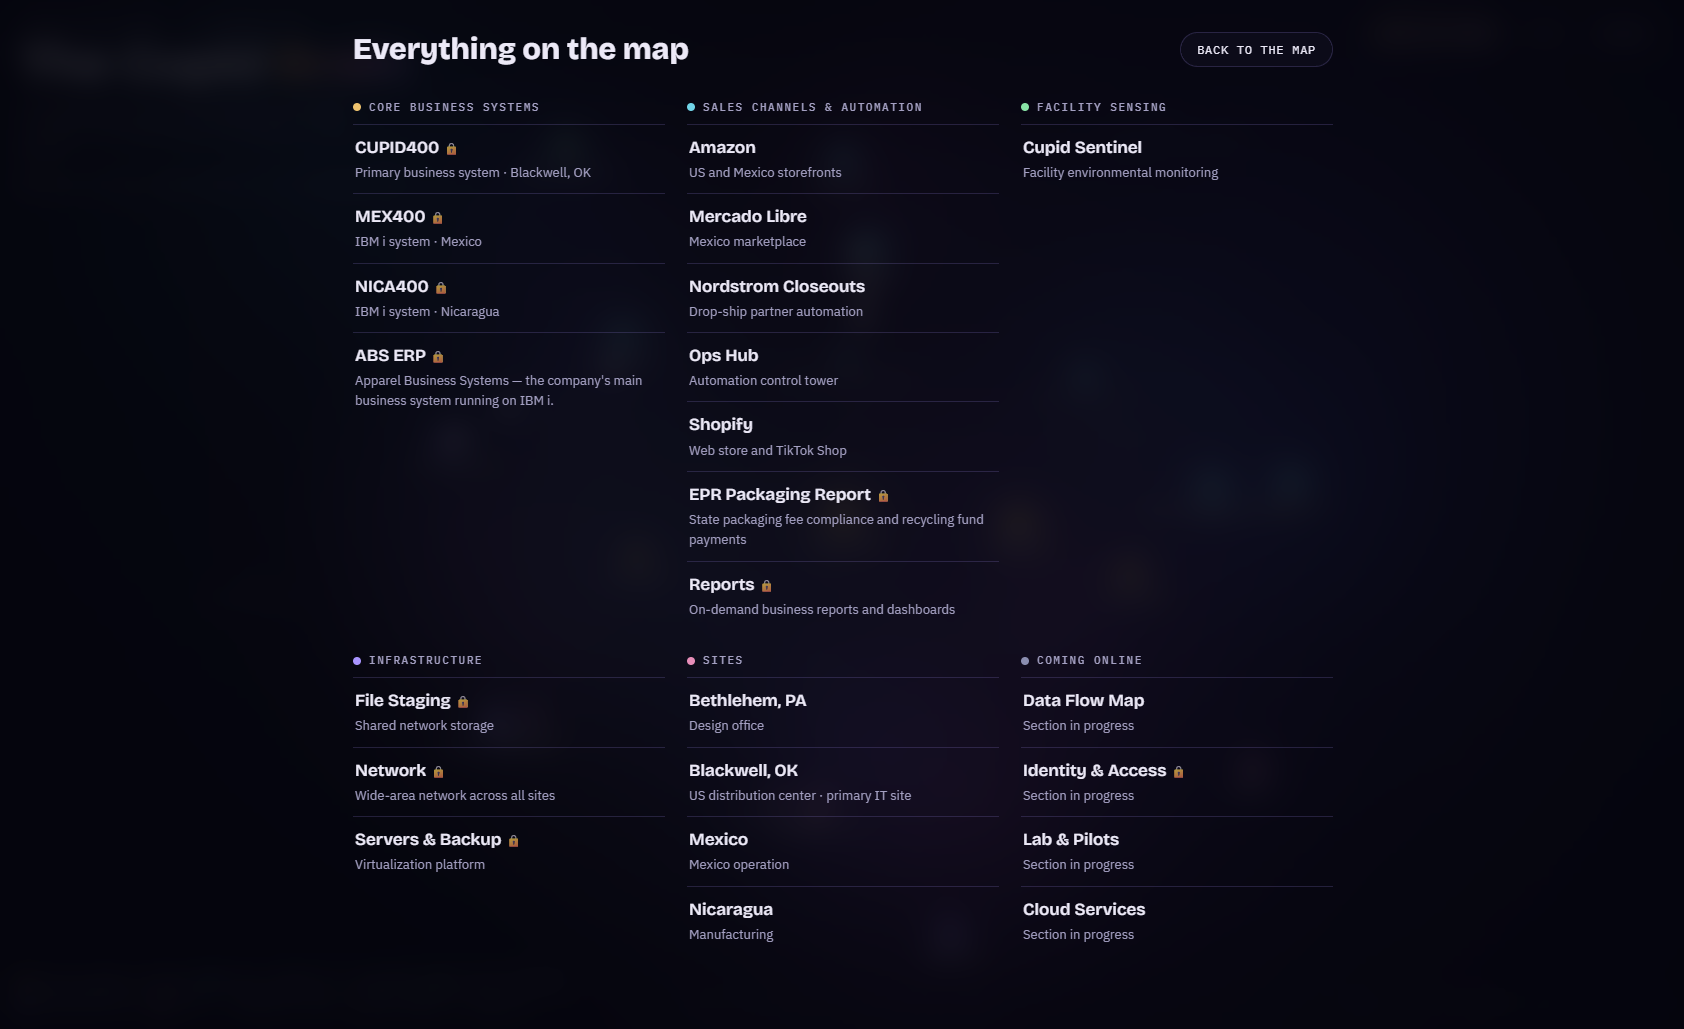
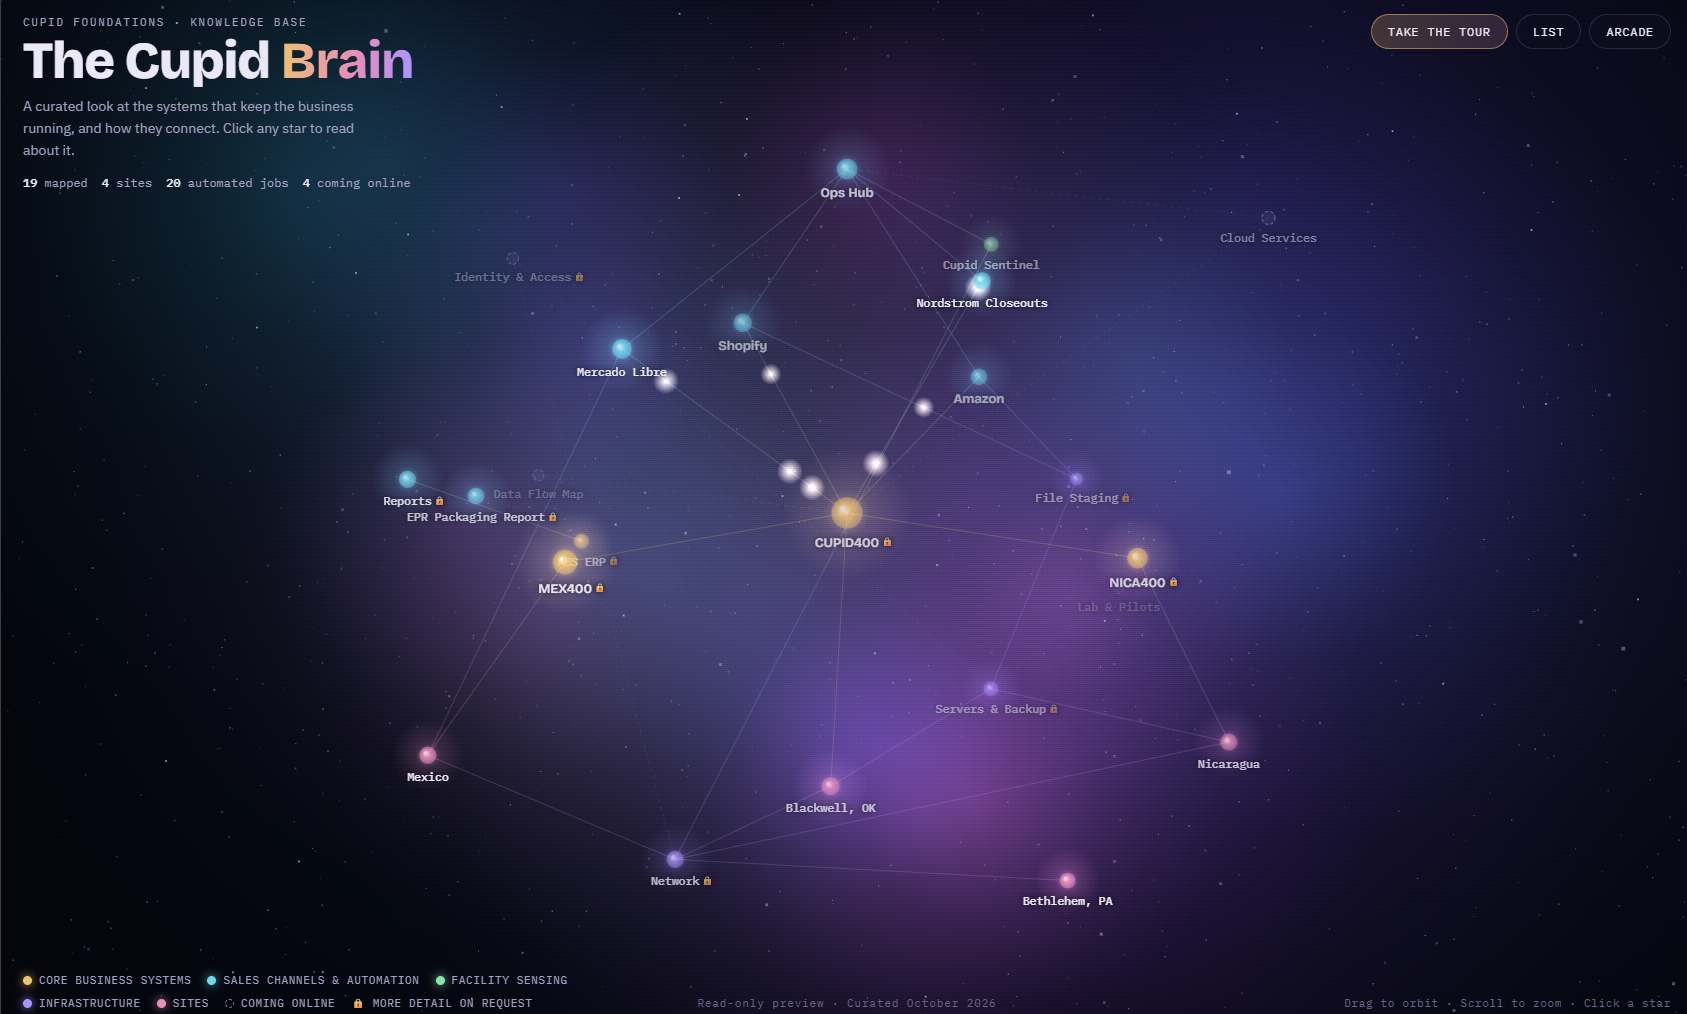
The result is a reference leadership and staff can actually use to understand how the business runs: which systems feed which sales channels, what runs on a schedule, what is in flight, and who to ask next.
Screens